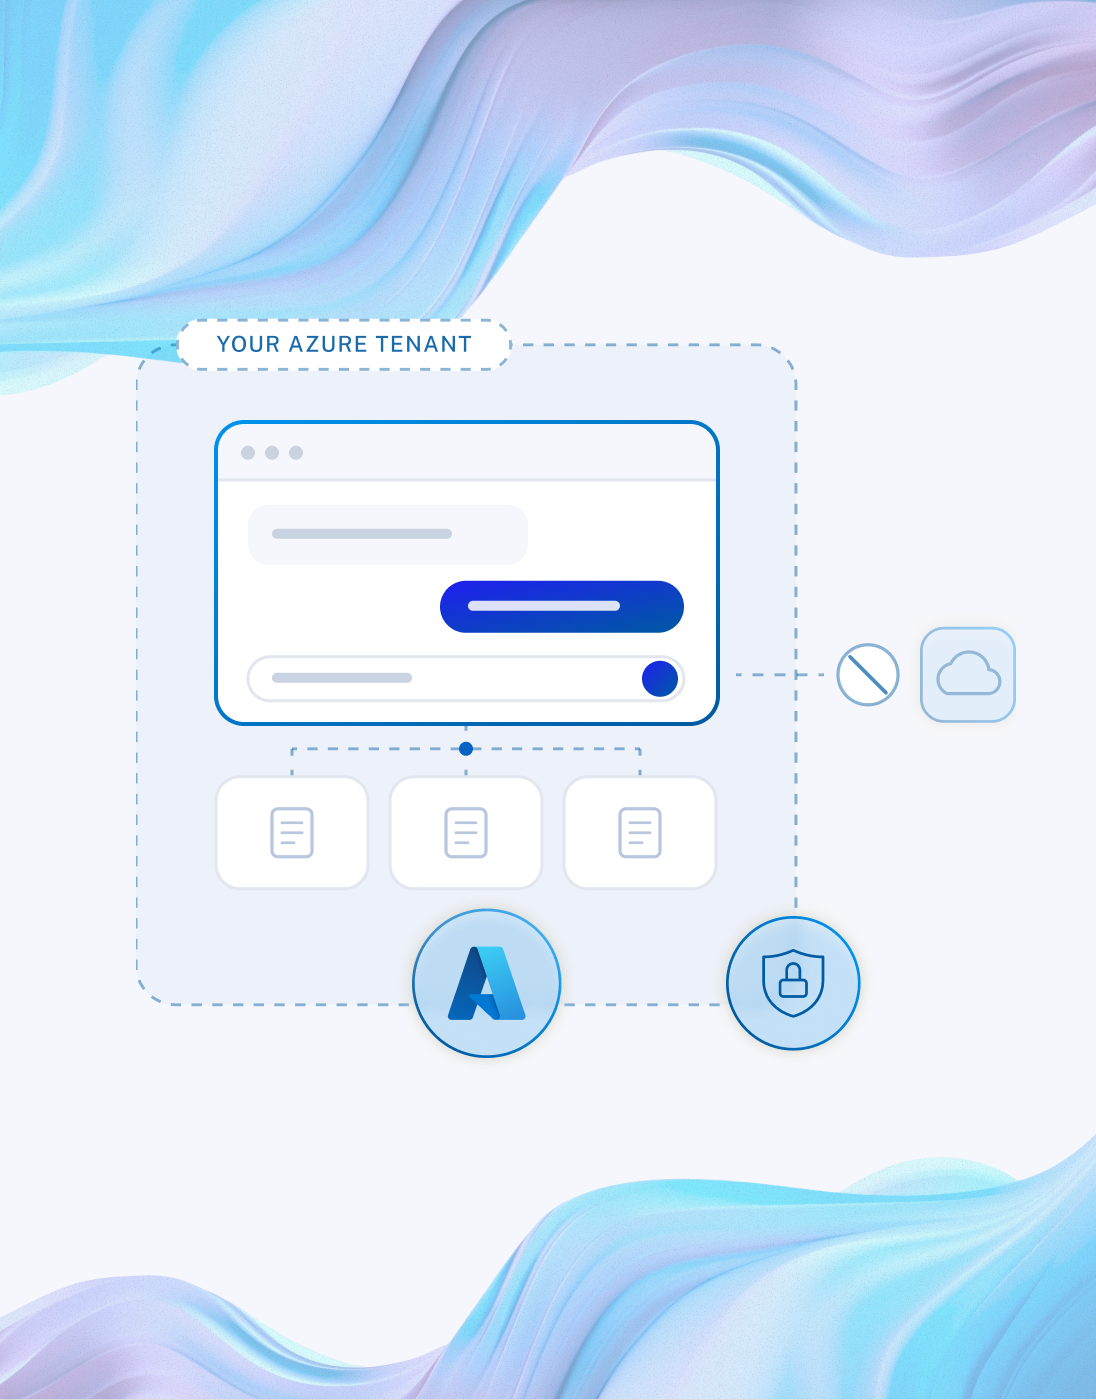
Your data never leaves your Azure tenant
nebulaONE® is designed to keep institutional AI work within your Microsoft Azure environment, with identity, access, data, and usage controls managed by your institution. Private by design, governed in practice.
Architecture & security features

Private Azure tenant
nebulaONE is deployed directly into your institution’s own Microsoft Azure tenant, not a shared multi-tenant cloud environment. Your data, your models, your infrastructure. There is no co-mingling with other institutions’ data, and no path for your institutional information to reach an external vendor’s servers.

No public exposure
nebulaONE operates entirely behind Azure private endpoints, meaning your deployment is never exposed to the public internet. All network traffic remains within your Azure environment, governed by your existing security perimeter and network policies. No new attack surface introduced.

No data training
Your institutional data is never used to train AI models by any party. What your faculty, staff, and students submit inside nebulaONE stays inside Microsoft Azure Cloud. You also decide which frontier models are available based on data residency terms set by Azure and each model provider.

Identity provider SSO
nebulaONE integrates natively with Microsoft Entra ID and supports SAML-based single sign-on so your existing identity infrastructure controls who can access the platform. No separate credentials, no shadow accounts, no new identity surface for your security team to manage.

Role-based access control (RBAC)
nebulaONE governs access through its own roles, groups, and access policies. Permissions can be scoped to your existing Microsoft Entra ID groups, so access mirrors the identity structure your institution already manages, without creating a second system to administer.

Audit-ready logging
Every conversation, model interaction, and agent session is logged and retained according to your institutional retention policy. Configuration audit logs capture all administrative changes giving your compliance team a complete, time-stamped record they can produce on demand.

Extensibility within your existing controls
Extend nebulaONE through the API, Claude Code, and OpenAI Codex to connect governed AI to approved applications and workflows. Keep access, data, and security policies under your institution’s control as use cases grow.
Buyer-centric compliance
SOC 2 Type I
Cloudforce maintains SOC 2 Type I compliance, providing independent third-party verification that our security, availability, and confidentiality controls are operating effectively. For enterprise IT and risk management teams, this means nebulaONE has already cleared the standard you require for mission-critical vendors in your environment.
HIPAA
nebulaONE includes HIPAA-aware controls for institutions managing health-related data including student health services, clinical programs, and research involving protected health information. The compliance boundary remains within your institution’s control, not a third-party vendor’s infrastructure.
FERPA
Student data handled through nebulaONE never leaves your institution’s Azure environment. Role-based access controls ensure that student-facing agents and data sources are accessible only to those with a legitimate educational interest aligned to FERPA’s need-to-know standard. Your registrar, legal counsel, and compliance office retain full control over what data is accessible, to whom, and under what conditions.
GDPR
For UK and EU institutions, nebulaONE’s architecture directly supports GDPR compliance by keeping personal data within the institution’s own cloud environment. There is no cross-border personal data transfer to a third-party vendor’s infrastructure. Institutions like the University of Surrey and Saïd Business School, Oxford operate nebulaONE under Microsoft’s UK and EU data residency commitments with no additional GDPR exposure introduced by the platform.
Public chatbots vs. private infrastructure
Evaluation factor
Public consumer chatbots
Our enterprise agent platform
Data usage
Data submitted by users may be ingested into public model training pipelines.
100% private: your data is never used to train models, by any party, ever.
Access control
Individual consumer accounts with no institutional governance, no SSO, and no role enforcement.
Centralized SSO via Microsoft Entra ID granular, role-based access controls across every agent.
Audit trails
Minimal or no enterprise-grade logging; no visibility into what institutional data was shared or by whom.
Complete audit logging across all conversations, agent interactions, and administrative changes that are exportable and retention-configurable.
See ONEchat in your tenant
We will walk your team through the chat experience, model configuration, and the admin controls — then show you exactly how deployment works inside your own Azure environment.
Address
120 Waterfront Street, Suite 500
National Harbor, MD 20745
Phone
202.803.6500
Media/Press Inquiries